- +971 56 918 6895
- sales@globaltechuae.com
- Salah Al Din Road, Deira, Dubai-UAE

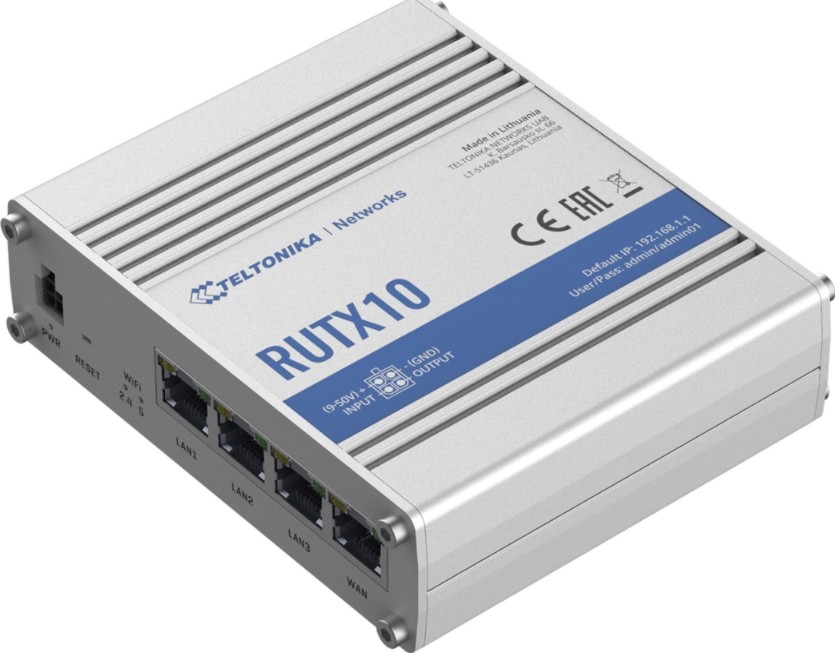
Teltonika Industrial VPN WiFi Router, Wifi and BT, 802.11ac (wifi 5) | RUTX10
د.إ 655.00
| Brand | Teltonika |
|---|---|
| Model | RUTX10 |
20
People watching this product now!
Description


| ETHERNET | |
| WAN | 1x WAN port (can be configured as LAN) 10/100/1000 Mbps, compliance with IEEE 802.3, IEEE 802.3u, 802.3az standards, supports auto MDI/MDIX crossover |
| LAN | 3x LAN ports, 10/100/1000 Mbps, compliance with IEEE 802.3, IEEE 802.3u, 802.3az standards, supports auto MDI/MDIX crossover |
| WIRELESS | |
| Wireless mode | 802.11ac (WiFi 5) with data transmission rates up to 867 Mbps (Dual Band, MU-MIMO), 802.11r fast transition, Access Point (AP), Station (STA) |
| WiFi security | WPA2-Enterprise-PEAP, WPA2-PSK, WPA-PSK, WEP; AES-CCMP, TKIP, Auto Cipher modes, client separation |
| ESSID | ESSID stealth mode |
| Wireless Hotspot | Captive portal (Hotspot), internal/external Radius server, built in customizable landing page |
| BLUETOOTH | |
| Bluetooth 4.0 | Bluetooth low energy (LE) for short range communication |
| NETWORK | |
| Routing | Static routing, Dynamic routing (BGP, OSPF v2, RIP v1/v2, EIGRP, NHRP) |
| Network protocols | TCP, UDP, IPv4, IPv6, ICMP, NTP, DNS, HTTP, HTTPS, FTP, SMTP, SSL v3, TLS, ARP, VRRP, PPP, PPPoE, UPNP, SSH, DHCP, Telnet client, SNMP, MQTT, Wake on LAN (WOL) |
| VoIP passthrough support | H.323 and SIP-alg protocol NAT helpers, allowing proper routing of VoIP packets |
| Connection monitoring | Ping Reboot, Wget reboot, Periodic Reboot, LCP and ICMP for link inspection |
| Firewall | Port forwards, traffic rules, custom rules |
| DHCP | Static and dynamic IP allocation, DHCP Relay, Relayd |
| QoS / Smart Queue Management (SQM) | Traffic priority queuing by source/destination, service, protocol or port, WMM, 802.11e |
| DDNS | Supported >25 service providers, others can be configured manually |
| Network backup | VRRP, Wired and WiFi WAN options, each of which can be used as an automatic Failover |
| SSHFS (optional) | Possibility to mount remote file system via SSH protocol (not available in standard FW) |
| SECURITY | |
| Authetication | Pre-shared key, digital certificates, X.509 certificates |
| Firewall | Pre-configured firewall rules can be enabled via WebUI, unlimited firewall configuration via CLI; DMZ; NAT; NAT-T |
| Attack prevention | DDOS prevention (SYN flood protection, SSH attack prevention, HTTP/HTTPS attack prevention), port scan prevention (SYN-FIN, SYN-RST, X-mas, NULL flags, FIN scan attacks) |
| VLAN | Port based and tag based VLAN separation |
| WEB filter | Blacklist for blocking out unwanted websites, whitelist for specifying allowed sites only |
| Access control | Flexible access control of TCP, UDP, ICMP packets, MAC address filter |
| VPN | |
| OpenVPN | Multiple clients and a server can run simultaneously, 12 encryption methods |
| OpenVPN Encryption | DES-CBC, RC2-CBC, DES-EDE-CBC, DES-EDE3-CBC, DESX-CBC, BF-CBC, RC2-40-CBC, CAST5-CBC, RC2-64-CBC, AES-128-CBC, AES-192-CBC, AES-256-CBC |
| IPsec | IKEv1, IKEv2, with 5 encryption methods for IPsec (DES, 3DES, AES128, AES192, AES256) |
| GRE | GRE tunnel |
| PPTP, L2TP | Client/Server instances can run simultaneously |
| Stunnel | Proxy designed to add TLS encryption functionality to existing clients and servers without any changes in the program’s code |
| DMVPN | Method of building scalable IPsec VPNs |
| SSTP | SSTP client instance support |
Related products


